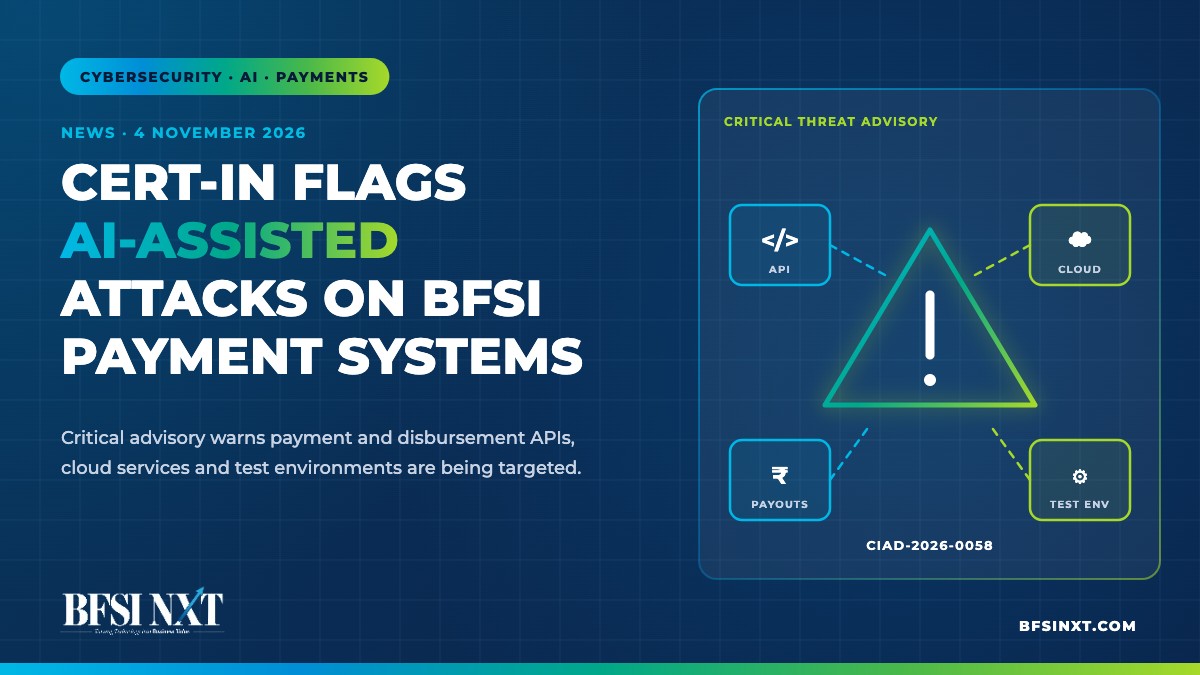
CERT-In has issued a critical-severity advisory describing an escalating campaign attributed to the threat actor it calls CRAFTY FALCON. The advisory warns that financial entities are being targeted through payment and disbursement APIs, cloud services and exposed environments.
The Indian Computer Emergency Response Team (CERT-In), through its financial-sector response function, issued advisory CIAD-2026-0058 on 4 November 2026. It describes an escalation in AI-assisted attacks against non-banking financial companies, digital lending platforms, fintech entities, payment aggregators, payment service providers and cryptocurrency-related businesses.
CERT-In has designated the threat actor as CRAFTY FALCON. The advisory says the campaign uses publicly available offensive security tools and machine-assisted techniques to survey targets, generate and refine scripts, adapt to target responses and exploit weaknesses in payment and disbursement systems.
The agency warns that attackers have revisited organisations where earlier remediation was incomplete. The advisory highlights risks involving exposed APIs, internet-facing systems, cloud management services and non-production environments that are not adequately isolated from production infrastructure.
CERT-In’s guidance calls for continuous monitoring, stronger API and cloud security, separation of testing and production environments, careful review of privileged access and prompt reporting of suspicious activity through the prescribed channels.
Primary source — CERT-In Advisory CIAD-2026-0058, 4 November 2026: Read original report / announcement
Additional reporting — Reuters, 5 November 2026: Read original report / announcement
Editorial attribution: Independently written and edited by the BFSI NXT News Desk based on the source material linked above. Company statements, targets and forward-looking estimates are attributed to the respective organisation and are not presented as guaranteed outcomes.