8
By BFSINXT Editorial Team
Security Summary
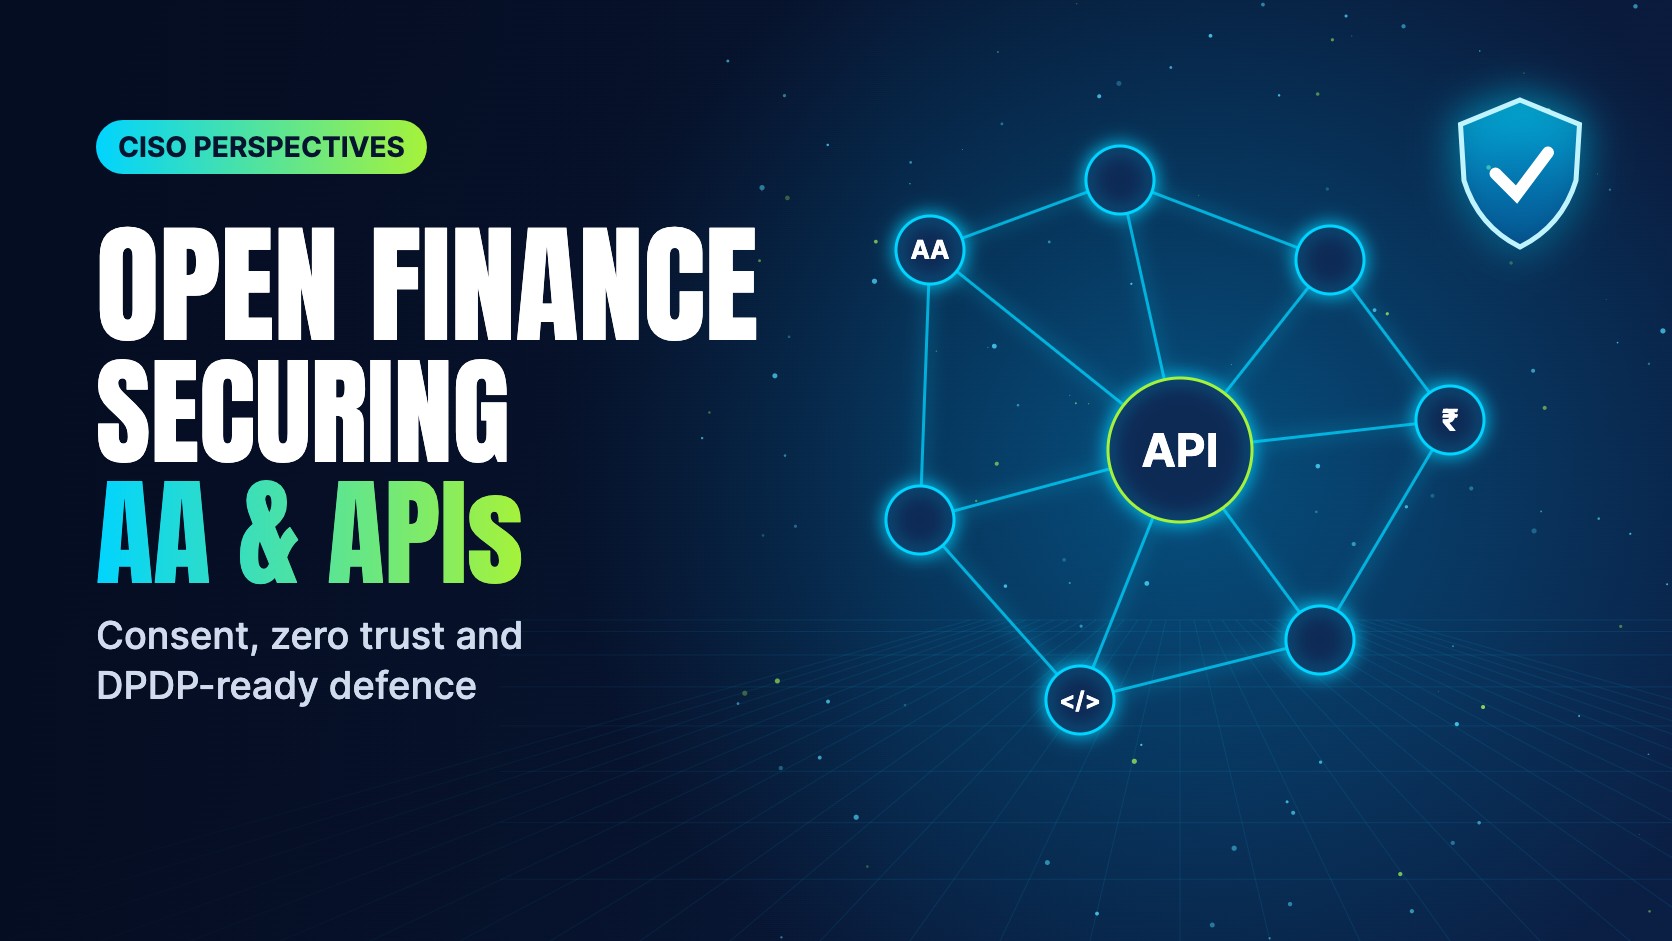
CISOs across Indian banks, payment aggregators, and fintechs address security challenges in an open banking economy. With the expansion of the Account Aggregator (AA) network and open APIs, security leaders highlight dynamic consent, zero-trust architectures, and API defenses under DPDP regulations.
Threat & Defense Focus Areas
- Transitioning from static OTPs to biometric passkeys and passwordless identity verification.
- Protecting open financial APIs against automated bot attacks, credential stuffing, and parameter tampering.
- Ensuring dynamic consent governance in line with Digital Personal Data Protection (DPDP) standards.