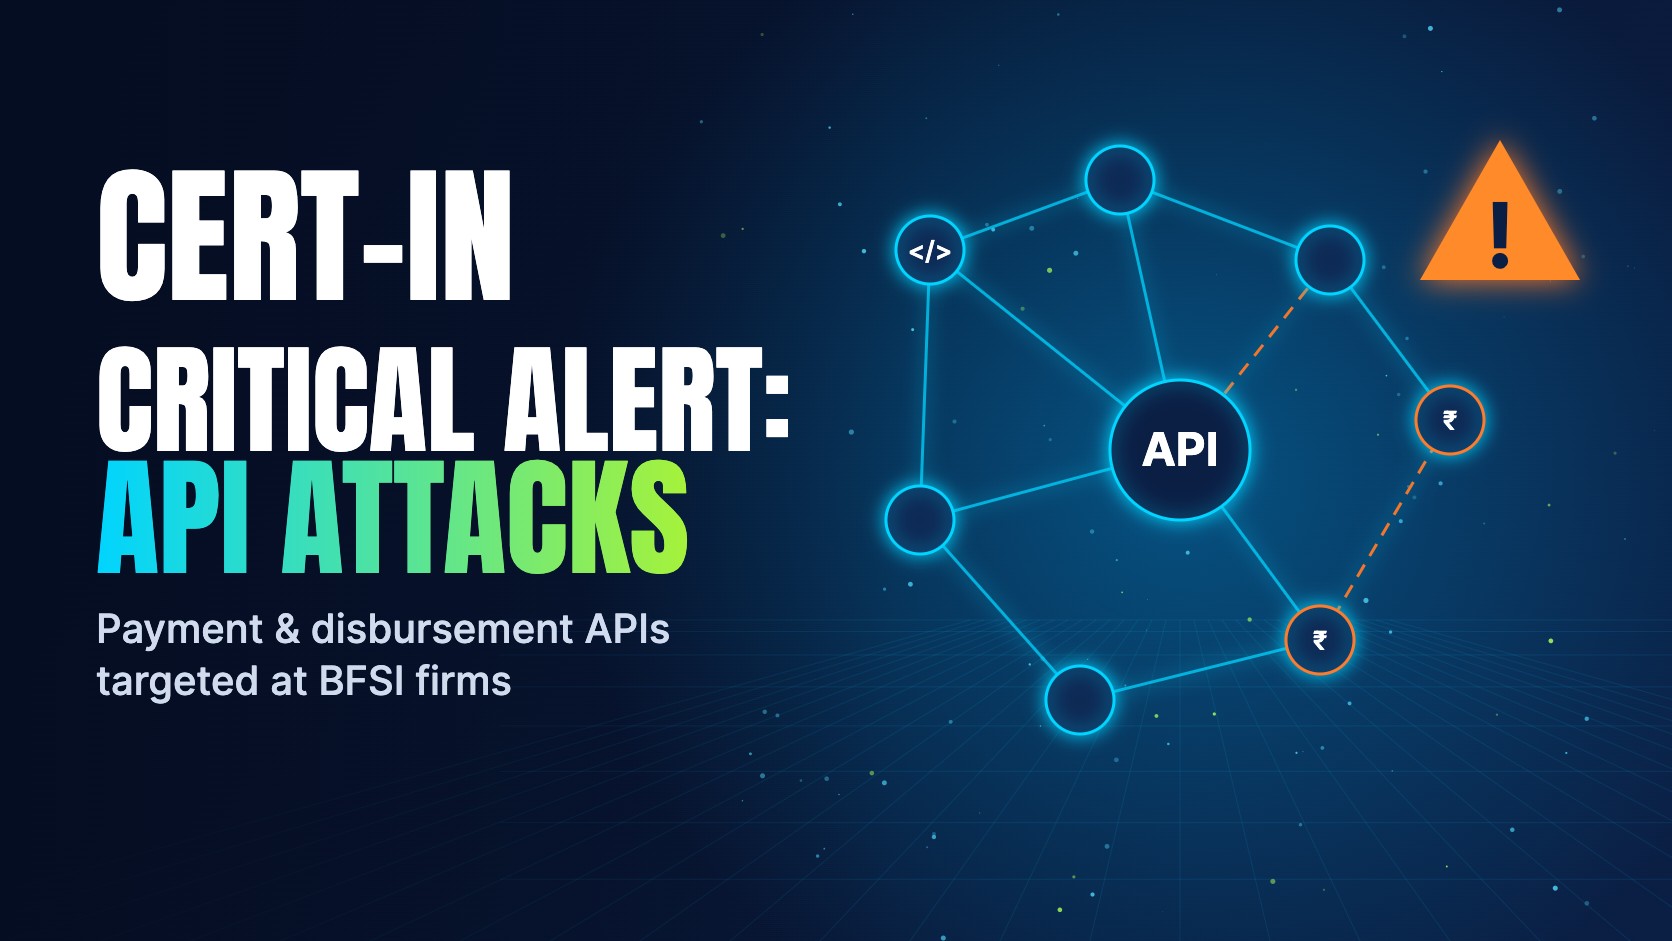
NEW DELHI, 9 October 2026 — CERT-In has issued a critical advisory describing cyberattack campaigns targeting NBFCs, digital lending platforms, fintech companies, payment service providers and wallet operators. The advisory warns that attackers may exploit exposed applications and APIs, steal credentials and attempt unauthorised fund transfers.
The advisory highlights risks including unused or poorly protected APIs, long-lived credentials, missing multi-factor authentication and payment workflows that do not consistently validate preceding approval steps. Such weaknesses can allow attackers to misuse legitimate access paths.
CERT-In recommends maintaining a complete API inventory, removing unused endpoints, strengthening authentication, securing credentials, enforcing maker-checker controls and monitoring fund transfers in near real time. BFSI organisations should review the advisory with their security, technology, fraud and operations teams.
Source: Indian Computer Emergency Response Team (CERT-In), Advisory CIAD-2026-0046. Rewritten and summarised by BFSI NXT. Please refer to the original source for full details.